
One Quote, 107 Tables, One Crit
A classic first-order SQLi in a legacy parameter, sqlmap, and 107 tables of very sensitive data. Target redacted.
Target, program, hostnames, rewards, and customer data are redacted. No rows were dumped; enumeration stopped at the schema. The bounty card below is the receipt.
Alhamdulilah another good HIT, this time a Crit.
It was a classic first-order SQLi that let me enumerate all 107 tables in the database. I didn’t want to share till the issue was resolved, cuz some of you smart folks might reverse engineer it or guess the program 😉.
This is concrete proof that although SQLi is rare nowadays, it doesn’t hurt to test it when your senses tell you to.
Details: after some time deep fuzzing I found some interesting paths on an interesting subdomain
(something-related-to-payments[.]term.
The data returned was interesting. You know the rest: sent it to sqlmap, no need for any crazy WAF
bypasses nor IP rotations, just old school CTF-like testing.
sqlmap -u "https://<redacted>/cgi-bin/<endpoint>.pl?term=France" \
  --prefix "'" --suffix "-- -" \
  --tables -D public --batch
It came back with boolean-based blind, time-based blind, and UNION. PostgreSQL backend, Apache, Perl CGI. Then I extracted 107 tables containing highly sensitive data such as payments, wallets, customer info, OTP tokens, and SSO sessions … the kind of stuff you see in a massive breach.
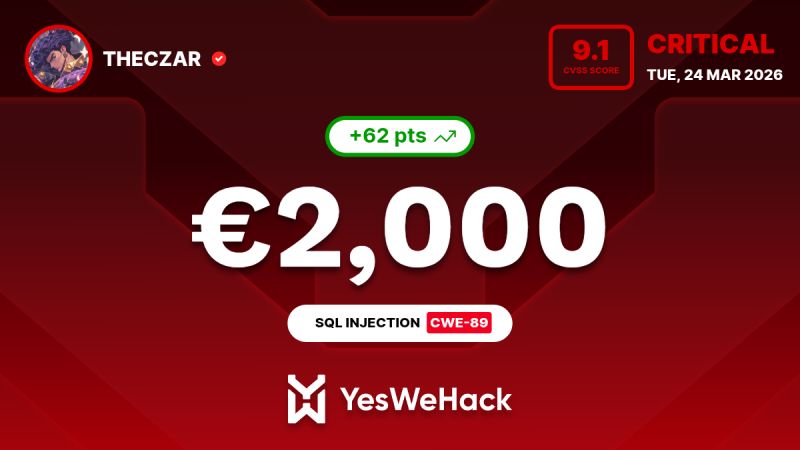
The bounty card: €2,000, Critical 9.1, CWE-89.
The issue was quickly resolved and rewarded, effectively saving the company’s data from a serious compromise.
Extra tips: most of you know recursive directory fuzzing, make sure to fuzz unusual status codes too such as 404 and 400, which most directory bruteforce tools skip by default, and don’t forget fuzzing extensions too.
Hope this was a useful read for yall and I didn’t waste your time. Cheers!